GLBA Regulation P and Consumer Opt-Out Rights
Regulation P's opt-out rules must now track data flowing through AI.
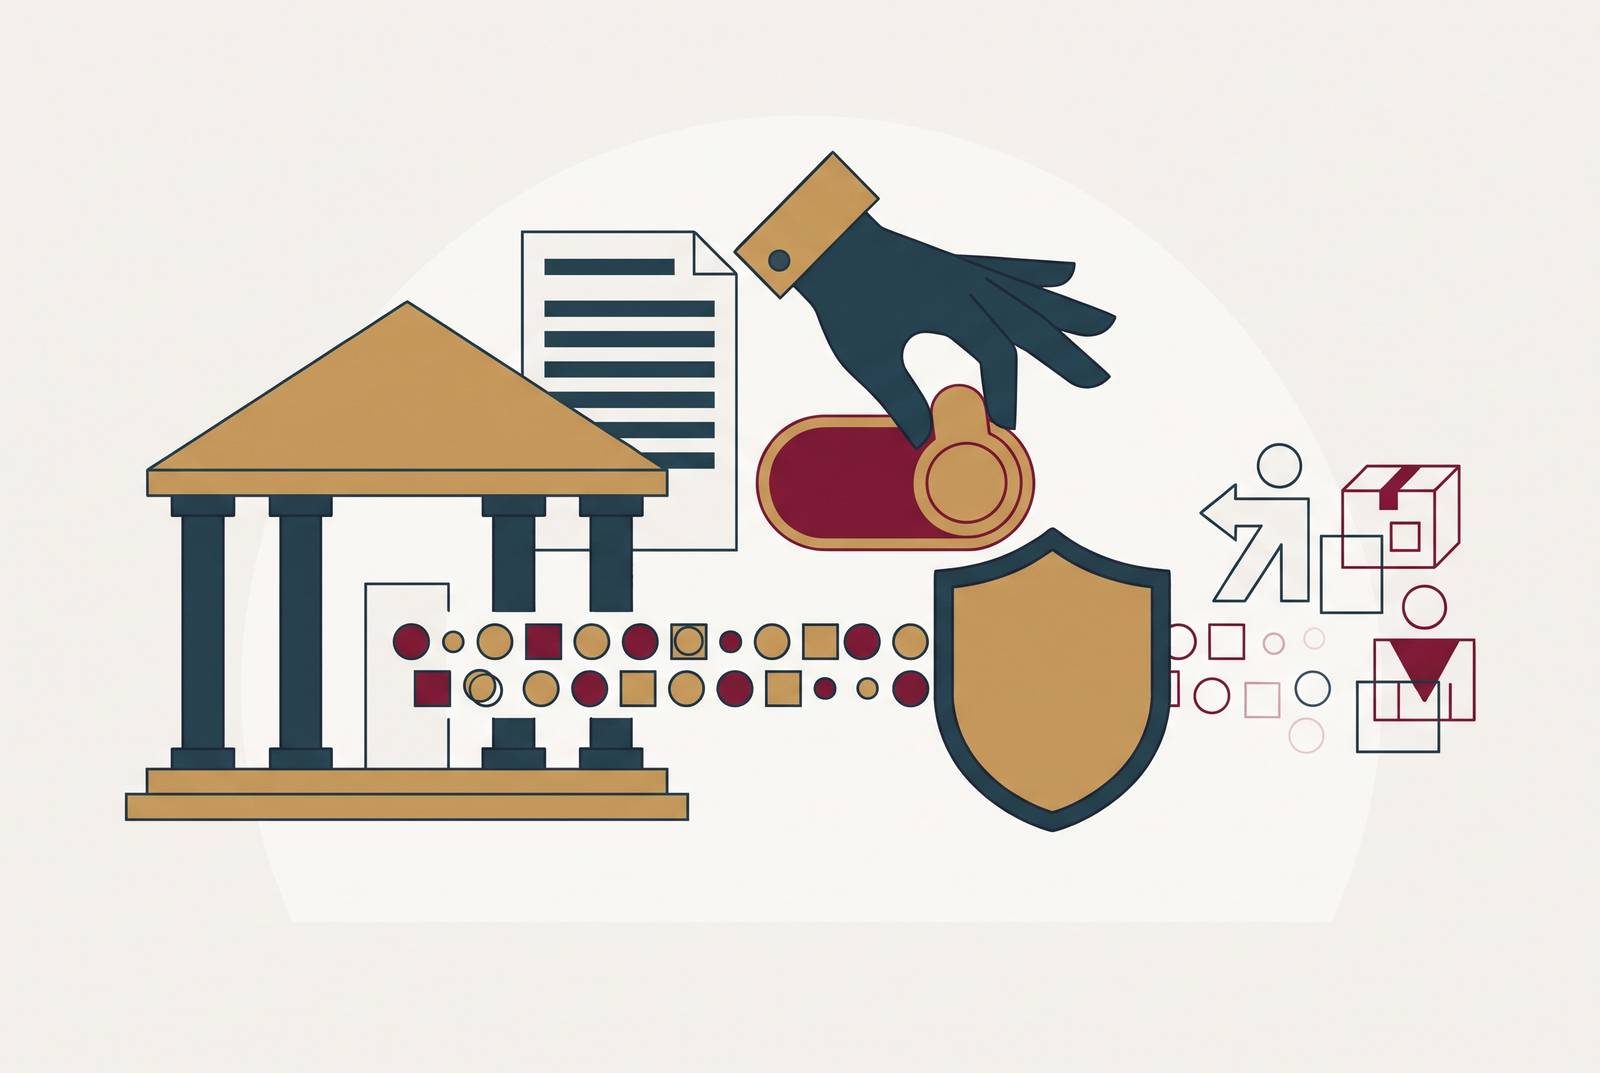
GLBA Regulation P gives consumers a right limited to restricting certain sharing of their financial information. Its framework rests on an opt-out default, required notices, and conditional exceptions. Bankers focused on compliance must apply those rules to how data actually flows, including through AI, as part of a program that goes beyond a privacy notice.
What Regulation P actually governs and what it does not
Regulation P protects nonpublic personal information, or NPI, about individuals who obtain financial products or services primarily for personal, family, or household purposes. Regulation P does not cover business-purpose relationships at all. NPI includes information a consumer provides, information resulting from a transaction, and information obtained in connection with providing a financial product or service, provided it is not publicly available.
Title V, Subtitle A of the Gramm-Leach-Bliley Act supplies the statutory basis. The CFPB recodified the implementing regulation, 12 CFR Part 1016, in December 2011 and administers it for most financial institutions. The OCC, FDIC, Federal Reserve, and NCUA enforce compliance at the institution level. The FTC’s Privacy Rule covers non-bank financial entities such as auto dealers and tax preparers, while the SEC administers Regulation S-P for securities entities, including broker-dealers and registered investment advisers.
The opt-out default: what it permits and what it costs the consumer who does nothing
Section 502 of GLBA starts with a prohibition on disclosure to nonaffiliated third parties, subject to exceptions. An institution can proceed when it has satisfied the notice and opt-out requirements and the consumer has not opted out. Silence then permits sharing within that framework. This is opt-out consent because the institution does not need an affirmative agreement before making a covered disclosure.
What does doing nothing cost the consumer? The consumer loses the opportunity to stop sharing that the rule allows them to restrict. Most consumers do not exercise the right, so the default, rather than an affirmative choice, governs the vast majority of NPI sharing with nonaffiliated third parties. An election, however, lasts until the consumer revokes it. It also continues to cover information collected during the relationship after the account closes. Sharing with affiliates follows a separate track, primarily under the Fair Credit Reporting Act.
Permission to share still has hard limits. In most cases, an institution cannot share account numbers with nonaffiliated third parties for telemarketing, direct mail, or email marketing. One of the limited exceptions lets it share with its own agent only to market its own products, as long as the agent cannot directly initiate charges. Recipients also face an onward-transfer restriction. A company receiving NPI cannot re-disclose it to others unless the originating institution could have made that disclosure itself.
The notice framework that makes the opt-out right operable
The initial privacy notice is due when the customer relationship is established. Before sharing outside the exceptions, the institution must also provide a clear and conspicuous opt-out notice, a reasonable means to exercise the right, and a reasonable opportunity to do so. Silence alone does not satisfy these requirements. The default becomes available only after the institution has supplied the notice and opportunity on which it depends.
Annual notices are generally required at least once in any period of 12 consecutive months during the customer relationship. The FAST Act created a specific exception, effective December 4, 2015, for institutions that share NPI only under the statutory exceptions and have not changed their practices since the last notice. Both conditions must be met to qualify. In a separate change, the CFPB’s October 2014 final rule allowed institutions to post annual notices on a website if they met certain conditions. Institutions eligible for that delivery method are effectively covered by the FAST Act exception as well.
The agencies’ two-page model privacy form is voluntary and gives institutions a safe harbor for what their notices say. Its “Why?”, “What?”, and “How?” structure explains sharing and provides a place to exercise available limits. But a form cannot substitute for accurate content. NCUA examiners check whether notices arrive on time, are accurate, clear and conspicuous, and are sent in a way that gives each member a reasonable chance of receiving actual notice. If practices change, the notice must change, regardless of how strong the institution’s security controls are.
The exceptions that permit sharing without an opt-out, and the conditions they carry
The exceptions cover much of routine banking, creating a substantial middle ground between prohibited disclosure and disclosure requiring an opt-out opportunity. Section 502(e) allows sharing when it is needed to process a transaction that was requested, service an account, prevent fraud or unauthorized transactions, or comply with law or legal process. It also covers disclosures with consumer consent, to a consumer reporting agency under the FCRA, and in connection with a business sale or merger. These disclosures do not require an opt-out notice. Their purposes either presume the consumer’s interest in the disclosure or reflect a legal requirement.
The service-provider and joint-marketing exception has a different set of conditions. Section 502(b)(2) permits sharing with a company performing services for the institution, including marketing its own products or products offered jointly with another financial institution. The institution must disclose this sharing in its privacy notice. It must also bind the provider by contract to keep the information confidential and use it only for the specified purpose. Those restrictions are mandatory conditions of the exception.
That distinction is especially important for AI vendors. A provider using shared NPI to improve its own commercial model may not qualify for the service-provider exception, even if it also performs a contracted service. Institutions deploying such vendors should examine whether the actual use stays within that service. An exception also does not remove the onward-transfer restriction. The recipient’s permission to receive information is not an unrestricted permission to pass it on.
Where honoring opt-out preferences becomes operationally difficult
An opt-out election creates an ongoing tracking obligation. The institution must apply it to future covered disclosures as well as to the data held when the consumer made the election. Connecting that durable preference to data that moves through changing systems poses an operational challenge. A record of the election is only the starting point.
When an AI vendor processes NPI, its handling of the data must remain consistent with applicable opt-out elections. A system sending behavioral or account data to a third-party model provider cannot treat opted-out consumers’ data like all other data unless an exception applies. Unauthorized tools create a more direct problem. An employee who copies NPI into such a tool causes a third-party disclosure outside the opt-out tracking system’s visibility. The institution cannot honor the consumer’s preference retroactively.
Machine learning can also make compliance harder to demonstrate. A model trained on aggregated customer data may embed NPI in ways that are difficult to isolate or reverse, leaving the institution unable to show that opted-out consumers’ data was excluded where required. Traditional logs were built to record separate transfers that could each be identified. Continuous training and inference pipelines do not create that kind of event record, so it is harder to prove compliance later. NCUA examiners check both whether an opt-out policy exists and whether institutions do what members have directed them to do.
What current Regulation P does not require institutions to disclose about how they process NPI
Regulation P’s notice framework describes categories of NPI collected and disclosed, categories of recipients, and policies and practices for protecting confidentiality and security. It is a sharing disclosure. It does not require explanations of internal uses, models or automated systems, derived inferences, retention periods, or secondary analytical purposes. That boundary reflects the framework’s focus on disclosure rather than the full life of information inside an institution.
A consumer can therefore read a compliant notice without learning whether transaction history trains a cross-sell targeting model, supports a churn score, or feeds an underwriting algorithm. The absence of that explanation is not itself a Regulation P notice violation. The American Bankers Association has tracked lawmakers’ work on this framework, including a March 2026 House Financial Services Committee hearing on updating financial privacy.
Legislative pressure on the current framework and what proposed changes would require
The GUARD Financial Data Act, H.R. 8398, was introduced April 21, 2026, and referred to the House Financial Services Committee. It is a companion to the SECURE Data Act, H.R. 8413. It remains a bill. The supplied reporting records no further legislative action, and its path is uncertain. Its proposals nevertheless show how far a revised framework could depart from current Regulation P.
One proposed change would require opt-in consent for sensitive NPI. That category includes racial or ethnic origin, religious belief, mental or physical health diagnosis, sexual orientation, citizenship or immigration status, precise geolocation, and genetic or biometric data disclosed to uniquely identify a consumer. Silence would no longer supply permission for that category. Existing opt-out systems would not satisfy the proposed requirement, because recording a refusal differs from obtaining affirmative consent.
The bill would also create deletion rights for former customers and impose new obligations on financial data aggregators. Its data-minimization standard would limit collection and disclosure to what is adequate, relevant, and reasonably necessary for a specified purpose. Current Regulation P has no equivalent deletion right. Current GLBA also imposes no data-minimization standard. A gap assessment would therefore reach beyond notice wording into consent architecture and deletion processes.
The ABA’s March 2026 statement before the House Financial Services Committee and June 2026 statement before the House Energy and Commerce Committee show how the industry is taking part in shaping reform. That engagement makes the proposed requirements useful preparation points, especially the requirement to describe categories of AI practices in collecting, processing, and using NPI. Meeting that proposal would require an inventory of AI tools and models touching NPI and plain-language descriptions of what they do with customer data.
What compliance-minded bankers should audit in their current Regulation P programs
Compliance teams should audit what they do now against the rules now in force and keep that work separate from preparing for proposed rules. A program that met examination requirements in 2020 may have gaps because data practices changed. Compliance teams should first check whether the privacy notice reflects actual third-party flows, including AI vendors, model providers, and analytics platforms. Institutions relying on the FAST Act exception should also confirm that sharing remains confined to statutory exceptions and that practices have not changed since the last notice.
For each nonaffiliated disclosure, the audit should identify either the applicable exception or the notice-and-opt-out path. Service-provider claims deserve scrutiny against the contract’s confidentiality and purpose restrictions. A vendor label is not enough by itself. Contracts with AI and analytics providers should be reviewed for uses that extend beyond the contracted service, especially training or improving a commercial model. The institution should also ask whether it can demonstrate that opt-out elections govern subsequent covered flows through automated systems.
Unauthorized tools require a separate control question. Can the institution prevent employees from disclosing NPI to third-party tools that sit outside its approved data environment? That exposure cannot be resolved by reviewing approved vendor contracts alone. A forward-looking inventory of AI and automated tools touching NPI can reveal ungoverned model risk and prepare the institution for a future disclosure requirement. This work helps with existing model-risk checks while keeping GUARD’s proposals separate from the law now in force.
Finally, every AI deployment raises an architecture question. Does it provide the visibility and controls needed to connect permitted uses, consumer preferences, and evidence of compliance? Purpose-built agentic banking platforms are designed for regulated environments and built to meet those accountability needs, with existing banking rails, configurable controls, and complete audit trails. The audit should check whether those capabilities meet the institution’s obligations.
Sources
- Gramm Leach Bliley Act (Reg P)
- Privacy of Consumer Financial Information (Regulation P)
- Regulation P Privacy of Consumer Financial Information BACKGROUND AND OVERVIEW
- ____________________ VIII. Privacy — GLBA Gramm-Leach-Bliley Act
- GLBA Privacy Notice Obligations
- 12 CFR Part 1016 - Privacy of Consumer Financial Information (Regulation P)
- How To Comply with the Privacy of Consumer Financial Information Rule of the Gramm-Leach-Bliley Act
- GLBA or FCRA? Data Sharing Between Affiliates and Non-Affiliates